Untangle Worth it for Home Network?

I was going after a low power usage setup. The motherboard is the Gigabyte GA-6KIEH-RH with a T9300 CPU and Intel NIC's in a 1U server case. It is now my dedicated Untangle server for home and plenty powerful.

BTW, jitter and latency WILL happen with VMware. Its whether your server is powerful enough to minimize it the point where it's not humanly noticeable.

Ahh, I was planning on using an AMD Zacate E-350, so that would have been significantly weaker than this :(
 
Zarathustra[H];1038268000 said:
Ahh, I was planning on using an AMD Zacate E-350, so that would have been significantly weaker than this :(

I bet you it would be just fine,
 
Go put words in your own mouth. I never said that.

You said this, did you not?
Untangle is about 1000 times simpler than a real firewall, .

Huh? HUH?

Or did someone "hijack your computer...log in....and type that using your account here?"

It clearly states you think it is not a real firewall.
If you considered it a real firewall, you would have worded it something like "Untangle is about 1000 times simpler than other firewalls". There is no back peddling here for you. I am not staff here, I don't have admin rights to go back and edit other users posts..The above is what you typed.
 
You said this, did you not?

Huh? HUH?

Or did someone "hijack your computer...log in....and type that using your account here?"

It clearly states you think it is not a real firewall.
If you considered it a real firewall, you would have worded it something like "Untangle is about 1000 times simpler than other firewalls". There is no back peddling here for you. I am not staff here, I don't have admin rights to go back and edit other users posts..The above is what you typed.

Grow up dude. I'm not backpeddling at all nor should I. You apparently would be offended no matter how I worded it, and you knew exactly what I meant. It's almost like you designed the product or something(??) Look....it IS simpler, and doesn't have the breadth of features of the firewalls I mentioned. It's a stateful firewall, and that's where the similarity ends. If you deny this, you deny reality.
 
Grow up dude. I'm not backpeddling at all nor should I. You apparently would be offended no matter how I worded it, and you knew exactly what I meant. It's almost like you designed the product or something(??) Look....it IS simpler, and doesn't have the breadth of features of the firewalls I mentioned. It's a stateful firewall, and that's where the similarity ends. If you deny this, you deny reality.

^^ cisco lover...
 
Look it up yourself, or take a class. It's not my job to educate you.

If it's not your job to educate us, then why are you speaking ? you started this...

Next time you start something like this, think about what you have to explain for the newb's or people that are trying to understand what your talking about..
 
If it's not your job to educate us, then why are you speaking ? you started this...

Next time you start something like this, think about what you have to explain for the newb's or people that are trying to understand what your talking about..

Seriously, grow the fuck up. I didn't start anything. I made a statement, that's it.
 
Seriously, grow the fuck up. I didn't start anything. I made a statement, that's it.

So back your statement up then. what are you 3 ? stop swearing, just shows that your the one that needs to grow up..
 
I think we can all calm down. I was just trying to give Valnar an oppurtunity to school some people. I was interested in what he sees as some of the big differences, just so I knew. If he doesn't wanna, fine.
Back on topic, an ASA vs FOSS for the home is going to heavily favor FOSS such as untangle, pfSense, IPcop, etc. There's a sticky at the top of this forum if you want a list and critiques.
 
[thread_hijack]

YeOldeStoneCat .. was wondering if you have used Smoothwall Express with the Advanced Web Proxy w/Urlfilter add-on .. if so, how does it compare with Untangle? ..is the url blacklist easy to update? ..is it broken into categories, ie.. porn,virusinfected,dating ...etc

..also , is it easy to add your own custom ip block lists (in mass, not one at a time) to Untangles IP block list?

..if your Untangle box is using dhcp off of your cable modem .. can you easily change your dns servers instead of using whatever the cable modem is giving you?

I'll probably just install Untangle and find these things out for myself I suppose .. I've been happy with my smoothwall setup , but I like to tinker and "play" with other distros when I get a chance. (just haven't had a chance in a long while).. but would be cool to know a couple things before I dive in.

thanks in advance

[/thread_hijack]
 
Last edited:
I bet you it would be just fine,

I'll give it a shot when I get the hardware, if for no other reason than to experiment with ESXi, but I am a bit concerned about the reports of jitter, especially since a lot of people play games in this house...

I'll put it together and compare jitter to my existing setup, and if it's no good, I'll just reformat the box as pfSense only...

At least that is my plan.

Have to recover financially from the holidays first. Spent WAY too much on gifts this year :rolleyes:
 
Zarathustra[H];1038270055 said:
I'll give it a shot when I get the hardware, if for no other reason than to experiment with ESXi, but I am a bit concerned about the reports of jitter, especially since a lot of people play games in this house...

I'll put it together and compare jitter to my existing setup, and if it's no good, I'll just reformat the box as pfSense only...

At least that is my plan.

Have to recover financially from the holidays first. Spent WAY too much on gifts this year :rolleyes:

That sounds like me too spent tons of gifts :(
 
Zarathustra[H];1038266845 said:
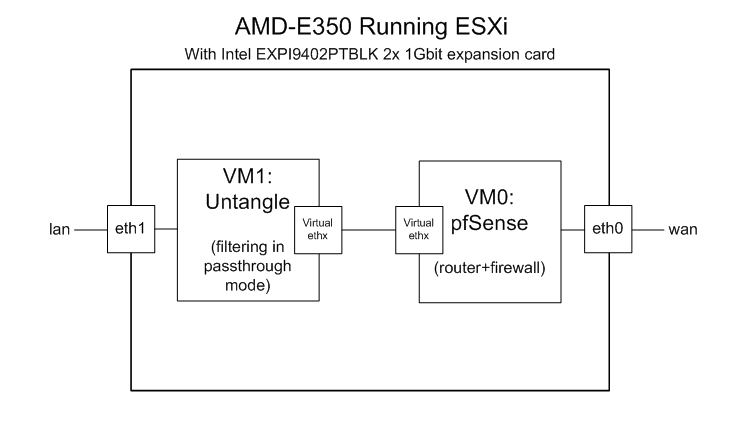
1.) Would the configuration look something like this?

6702746397_cbf37e80e7_o.jpg

Can anyone speak to how important it would be to have a system capable of IOMMU / VT-d for the NIC's to do the above?

What would I lose by running ESXi on a non-IOMMU capable machine? is it significant?
 
Didn't play with ad-ons back when I piddled with Smoothie
Didn't try adding custom I blocks ....are you looking to block incoming or outgoing?
Yes you can customize DNS no problem


[thread_hijack]

YeOldeStoneCat .. was wondering if you have used Smoothwall Express with the Advanced Web Proxy w/Urlfilter add-on .. if so, how does it compare with Untangle? ..is the url blacklist easy to update? ..is it broken into categories, ie.. porn,virusinfected,dating ...etc

..also , is it easy to add your own custom ip block lists (in mass, not one at a time) to Untangles IP block list?

..if your Untangle box is using dhcp off of your cable modem .. can you easily change your dns servers instead of using whatever the cable modem is giving you?

I'll probably just install Untangle and find these things out for myself I suppose .. I've been happy with my smoothwall setup , but I like to tinker and "play" with other distros when I get a chance. (just haven't had a chance in a long while).. but would be cool to know a couple things before I dive in.

thanks in advance

[/thread_hijack]
 
Zarathustra[H];1038298143 said:
Can anyone speak to how important it would be to have a system capable of IOMMU / VT-d for the NIC's to do the above?

What would I lose by running ESXi on a non-IOMMU capable machine? is it significant?

There is VERY little reason to pass through a physical NIC to something like Untangle. You lose a lot by doing that..like vMotion and DRS if you have licensing for those features. If your switch supports VLANs just use shared NICs w/ internal/external VLANs.

EDIT: Or create a port-group just for internal and one for external and add a NIC in to each...that way it's dedicated to only Untangle but not passed through and breaking things.
 
Didn't play with ad-ons back when I piddled with Smoothie
Didn't try adding custom I blocks ....are you looking to block incoming or outgoing?
Yes you can customize DNS no problem

just block incoming .. like the china,korea, list ..etc

Does the web filter lite update itself, or can I manually update it?( as far as the blocked web sites list)

I have installed now and giving it a go .. the x64 version on an Atom 230 setup w/4gb ecc DDR2 memory and 20gb xbox360 sata drive.

Doesn't seem to be as customize-able as smoothwall as of yet .. which is probably by design as part of their business model.. but I'm just starting to "play" with it and reading through the untangle forums and what not..
 
just block incoming .. like the china,korea, list ..etc

Does the web filter lite update itself, or can I manually update it?( as far as the blocked web sites list)

I have installed now and giving it a go .. the x64 version on an Atom 230 setup w/4gb ecc DDR2 memory and 20gb xbox360 sata drive.

Doesn't seem to be as customize-able as smoothwall as of yet .. which is probably by design as part of their business model.. but I'm just starting to "play" with it and reading through the untangle forums and what not..

There are occasional updates to the web filter..not like several times a day like AV definition updates.

In the Networking part...dig over on the right side, there's a drop down menu for advanced features which most people miss. That's where all the customizable stuff is. Single core Atoms are pretty painful.
 
small (couple computers, xbox, wii , couple laptops) home network .. so this ht enabled atom seems to be doing just fine fortunately.

with smoothwall you could go to urlblacklist.com and grab a 19mb txt file of categorized websites (1st download is free and then honor pay fee after that) that could be added easily to the urlfilter mod .. can I add such a list to web filter lite myself in mass?
 
What do those states look like? I'd really like to know what Steam is using at least 5 connections per server for.

I decided to challenge the system, cause I was curious.

In order to make it a worst case test, I set the steam bandwidth as high as it would go (still below my bandwidth), and I set pfsense's timeout behavior to "conservative".

I set pfsense to 1,048,576, because it is a nice round number that fits in the amount of RAM I have.

I then reset the state table, and proceeded to do a full unfiltered steam server refresh.

For me the state table peaked at about 40,000 entries.


So, 1,048,576, seems like it should be enough for now :p
 
Back
Top