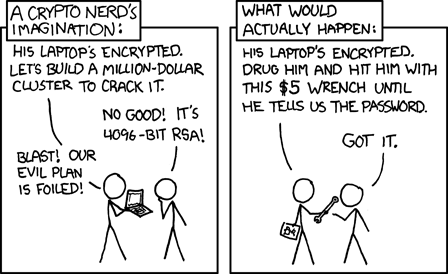
Do you think they would actually disclose this?
Chances you'd be on the NSA list to have your volume cracked in the first place is low.
We do know the FBI has tried and failed.
http://www.theregister.co.uk/2010/06/28/brazil_banker_crypto_lock_out/
With a proper random password of 20+ characters with mixed upper, lower, numbers, and symbols, I'd like to see the NSA try it with every computer on earth. The formula doesn't lie and we can break down a single computers potential on a local machine. There are really only 3 ways to break it before the end of the world:
1) Weakness in the algorithm
2) Flaw in the software implementing the algorithm
3) Flaw in the operating system
Of course there are many other parts in the chain that can theoretically leave open vulnerabilities, but those are the 3 big ones that every user must trust.